Defensive. Authorized use only.
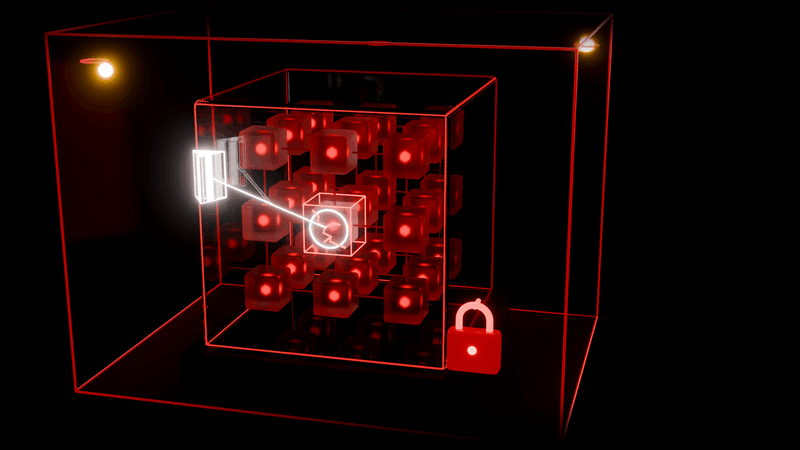
Private security AI
OmniConflux Red Team is frontier-class security AI, privately hosted on private single-tenant servers for defensive, authorized security work. We run it on our own systems every day. The closed beta is open now, and every access request is reviewed before anything is provisioned.
A flaw, from found to fixed.
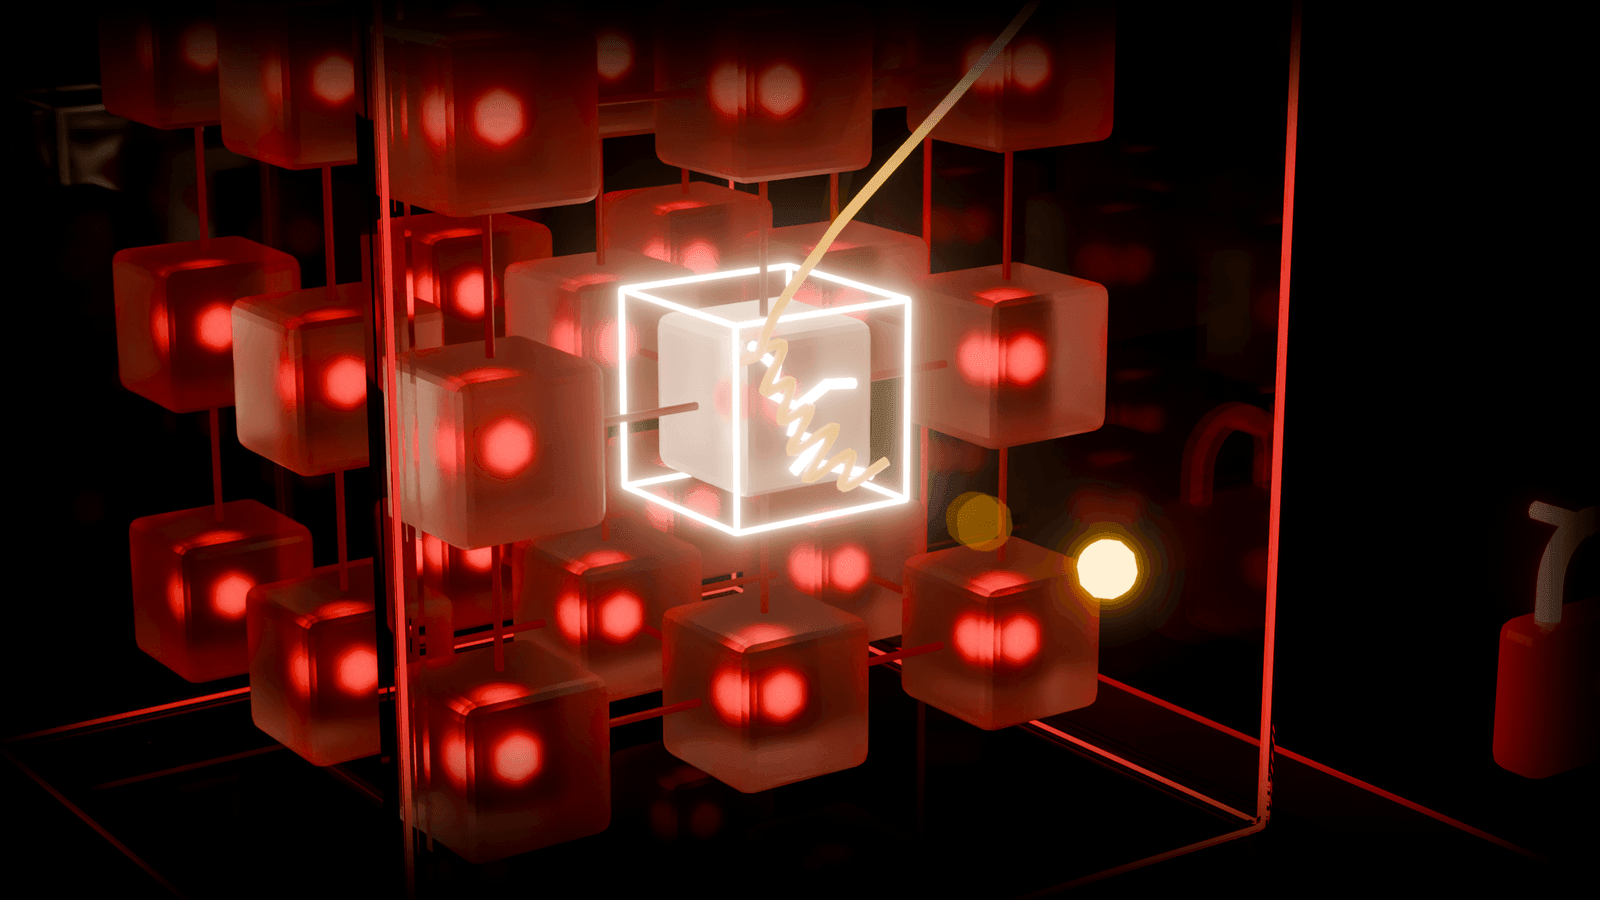
OmniConflux Red Team runs on one loop: test, find, prove, fix, re-test. This illustration walks through it in five steps.
The vault.
Under test
The lattice stands for your systems, inside a private, locked enclosure. Gold probes and a scan frame test each one.
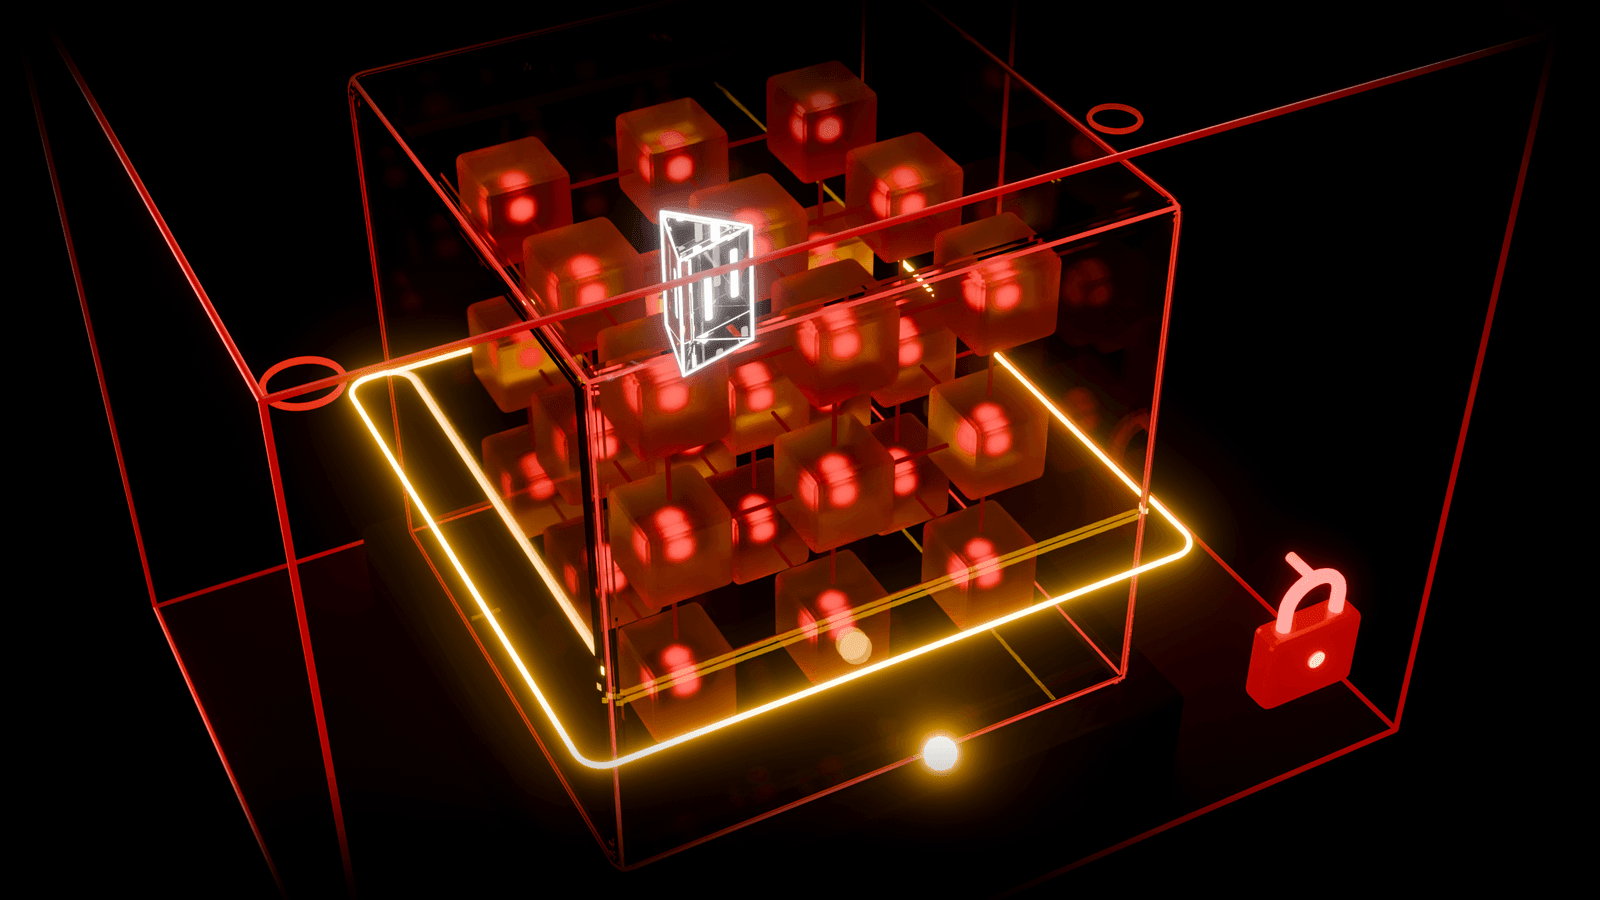
Flaw found.
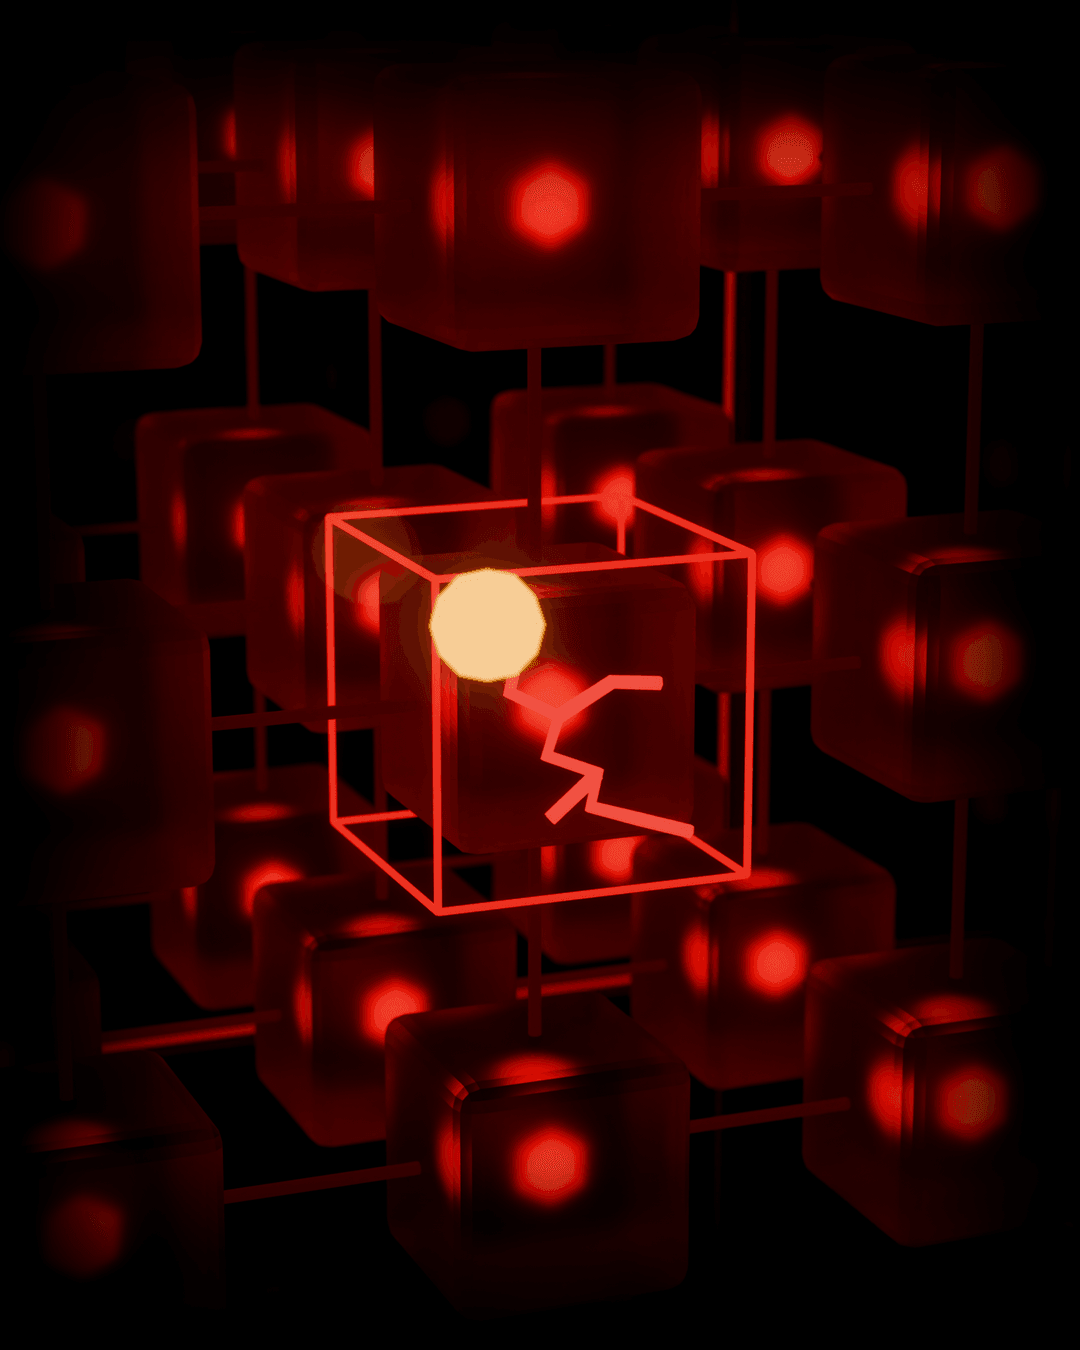
One probe holds at a single system. A hairline crack turns red.
Flaw
Proven.
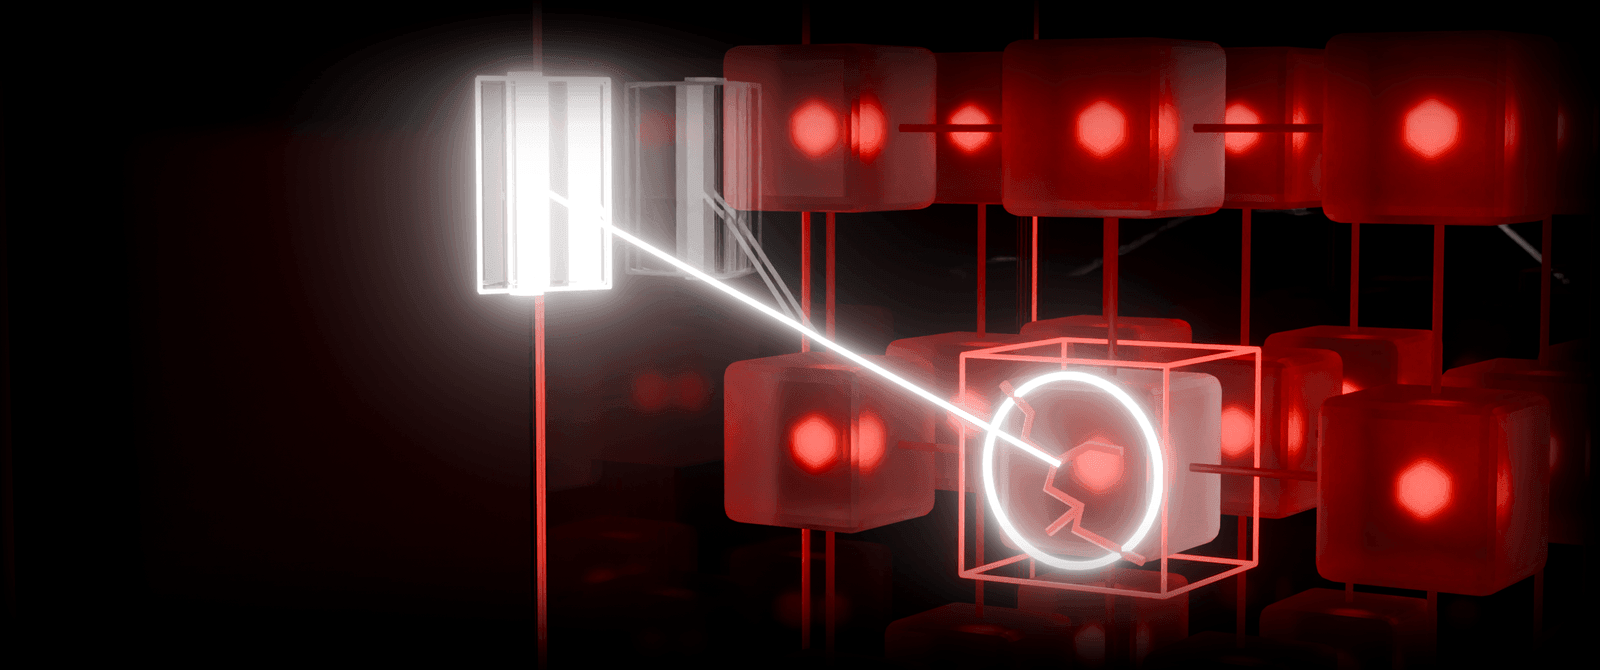
A verification prism checks the crack. A white ray and ring confirm the flaw is real before any fix.
Verified
Patched.
A gold patch strand comes down and stitches across the crack.
Patch
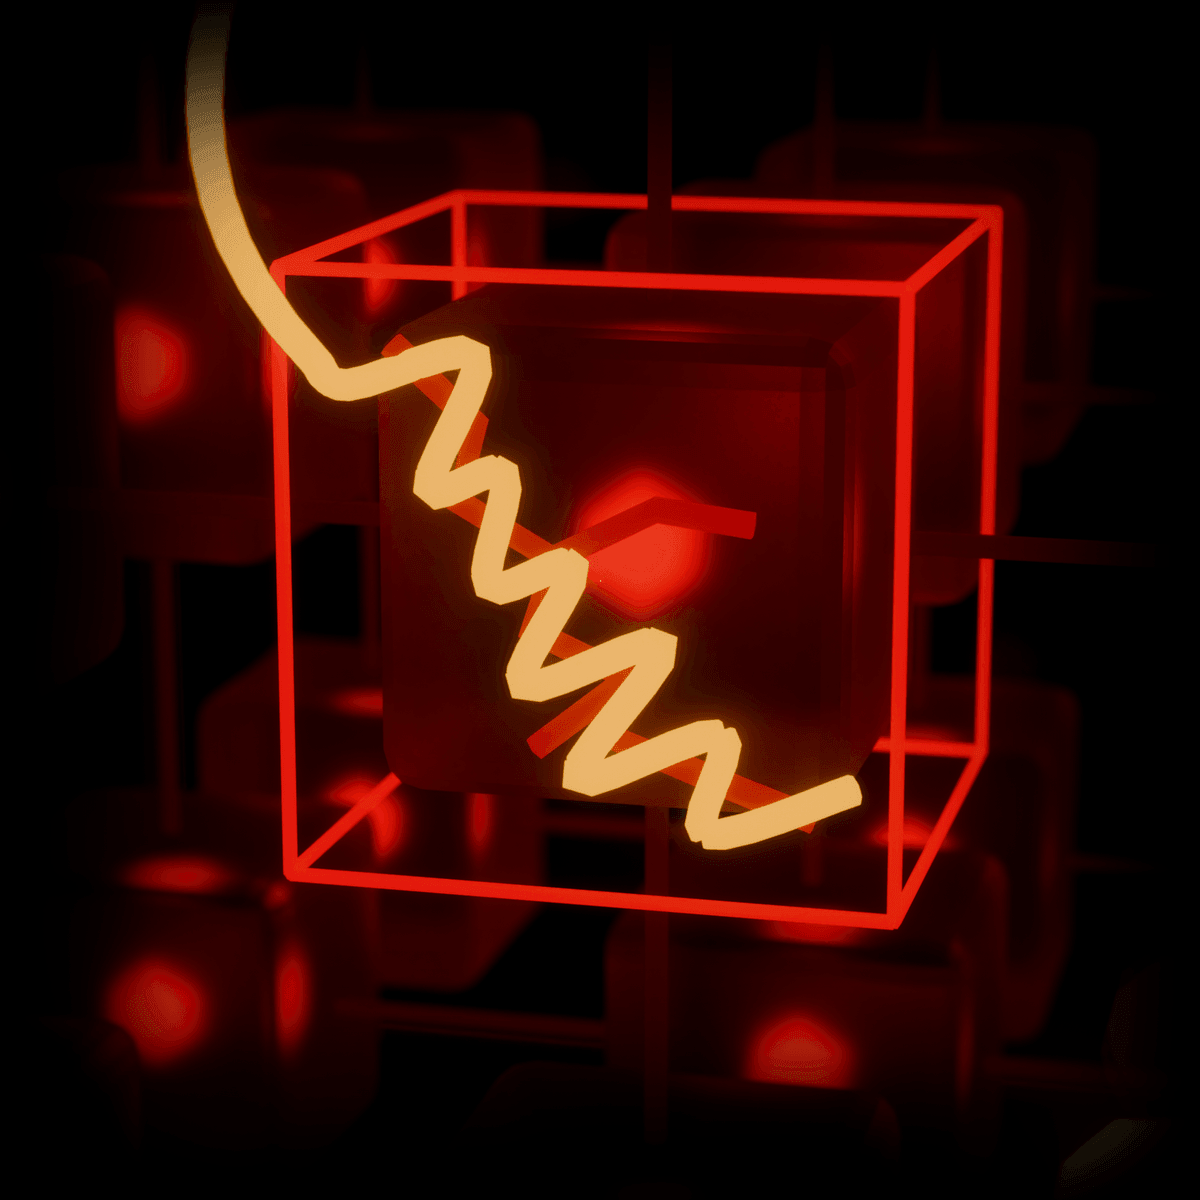
Re-tested.
A second probe tests the patch. The crack turns white-gold, and the vault settles.
Fixed
OmniConflux Red Team
Access is limited to defensive work on systems you own or have written authorization to assess. Every request is reviewed before provisioning.
- 1
Written authorization
Document permission and the agreed scope before any security work begins.
- 2
Acceptable-use policy
Accept the policy before provisioning. Unauthorized access and activity outside the approved scope are prohibited.
- 3
KYC before provisioning
Identity and organization verification is required before any private single-tenant server is provisioned.
Request access
Start with authorization.
Tell us about your organization. A request does not grant access or permission to assess any system.